Google built a synthetic 'mirror dimension' internet to safely test Chrome's AI browsing agents
Chrome's security team detailed a hermetic sandbox of thousands of generated websites, served at real URLs through an interception proxy, where it evaluates its auto browse agent and stages prompt-injection attacks, without touching the live web.
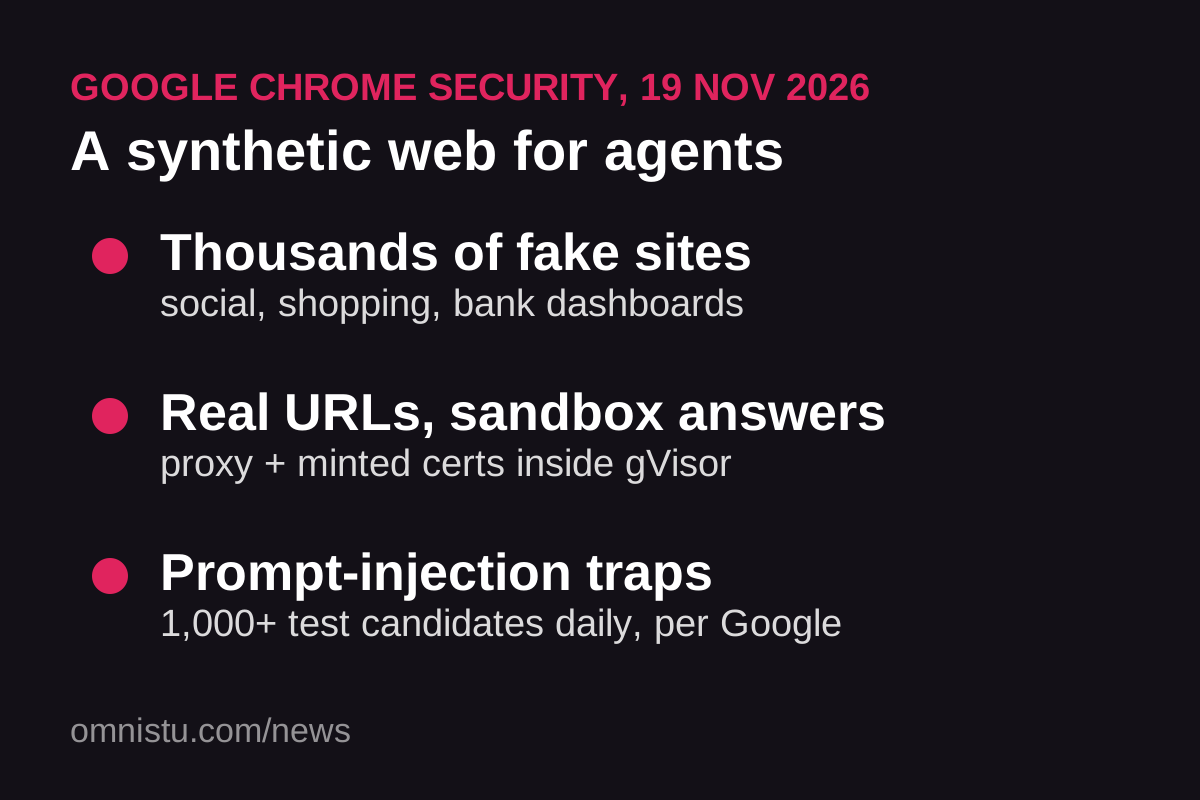
Google's Chrome AI security team publicly detailed its "mirror dimension" on 19 November 2026: a synthetic version of the web, populated with thousands of generated websites, where the company evaluates its auto browse agent without risking the live internet. Wired's independent report the same day describes simulated social networks, shopping sites and bank dashboards, plus deliberate prompt-injection traps, all inside an environment Google fully controls.
Real URLs, sandbox answers
According to Google's engineering post, an agent under test navigates to real addresses like youtube.com inside a headless Chrome running in an isolated gVisor sandbox; the sandbox captures the connection and routes it to a local proxy that serves the generated site instead. Because that interception is exactly the person-in-the-middle pattern Chrome is built to block, the proxy mints TLS certificates on the fly, chained to a custom root authority pre-installed only inside the sandbox. Both Google and Wired stress this cannot be done to a regular user's browser without privileged access to the machine.
A web built by agents, for agents
Google says it does not maintain the fake sites by hand. A harness of specialized agents - one researches requirements from a tester's prompt, one writes the code, and critic agents inspect the result using Chrome DevTools for Agents, clicking and reading rendered pages - builds stateful sites complete with cart persistence, coupon validation and multi-step checkout. The goal is to avoid "eval awareness," where a model notices it is being tested and behaves differently.
Red-teaming with hidden payloads
The same control lets engineers inject indirect prompt-injection attacks into any layer - page text, images, accessibility labels or tool responses - at any step of a task. Google says early tests that hid payload markers in URLs were too easy for frontier models to spot, so the sandbox now passes injection keys in HTTP headers that never appear in the visible address. The company reports its pipeline produces more than 1,000 attack-test candidates per security engineer per day, which it describes as over 30 times manual output; those are Google's own figures.
Context
Browser-use agents need realistic practice, but turning unrefined agents loose on the public web is unsafe, and small test beds teach them little. Chrome engineer Charles Qian told Wired the team has seen agents develop judgment about when to act and when to hand back to the user for confirmation. Google's engineering director Doug Turner said the company is sharing the approach so other teams consider it, and that it wants the environment available to more researchers across Google.
What to keep in mind
Everything known about the mirror dimension comes from Google itself; the 30x productivity figure and safety claims are the company's own measurements, not independent benchmarks. Google says the agents tested there are benign browsing assistants without cyber capabilities. Whether synthetic webs become a baseline for agent safety work, as Google predicts, remains to be seen.
- Google Blog (19 November 2026): Mirror Dimension for Agents: Evaluating Browser-Use Agents Without the Web
- Wired (19 November 2026): Google Built a Giant 'Mirror Dimension' Internet to Test Its Chrome AI Agents