European Commission confirms an AI-assisted cyberattack hit its personnel systems
The Commission confirmed on 19 November that attackers used AI tools in a campaign first detected on 22 October, disrupting payroll, leave, medical reimbursement and translation systems for more than 10 days. CERT-EU identified the open-source ARTEX framework, according to POLITICO, days after an FBI warning about it.
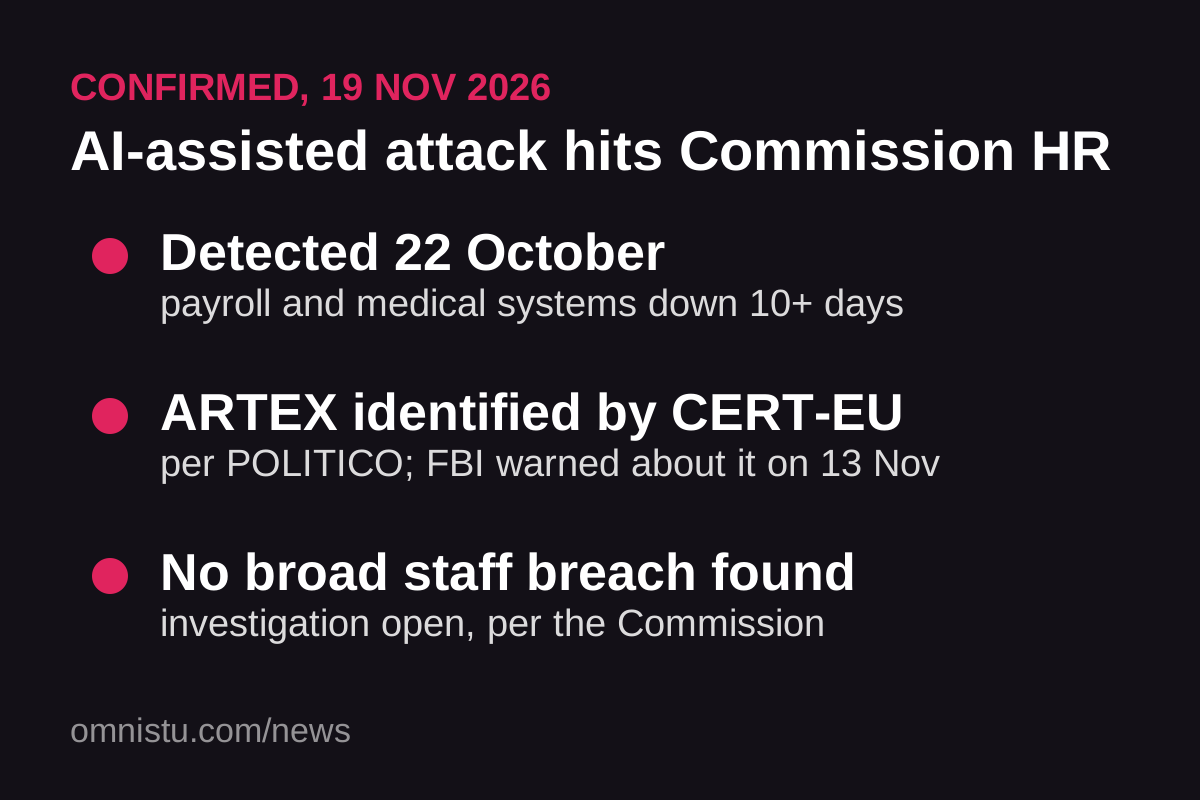
The European Commission confirmed on Thursday 19 November 2026 that it was hit by a cyberattack last month involving a publicly available AI tool, the first time the 27-member bloc has reported an attack using one. Spokesperson Thomas Regnier said the first signs were detected on 22 October and described it as an "AI-generated cyber campaign", but did not name the tool or the attackers' motivation. POLITICO, which first reported the incident, said CERT-EU had identified the attackers' use of ARTEX, an open-source AI penetration-testing framework.
What was disrupted
The attack reportedly disrupted the Commission's personnel systems for more than 10 days, including payroll, leave requests, medical reimbursements and translation services. Regnier said several applications were taken offline "as a protective and preventive measure" and most have since been restored. He said investigators found no evidence of a data breach affecting Commission staff as a whole, were unaware of any ransom demand, and that the investigation remains open. Affected individuals were notified, and the European Data Protection Supervisor was informed. "There was no hiding whatsoever," he told journalists, saying publicizing defensive measures earlier could have undermined them.
The FBI warning about ARTEX
The confirmation came barely a week after a 13 November FBI advisory about ARTEX, which it described as an autonomous penetration-testing framework in use by malicious actors since at least August 2026 across sectors including government, finance, energy, healthcare and technology. The FBI said some intrusions progressed from initial targeting to privileged access in under three hours. The framework, released in July, uses commercial AI models to automate vulnerability discovery and exploitation; GitHub made it unavailable on 8 October, but the FBI said it remains accessible through mirrors.
Context
It is the Commission's third disclosed cyber incident this year, after breaches involving Ivanti software in January and its cloud infrastructure in March; officials have not linked the incidents. The Record notes the incident follows a June Five Eyes alert that AI would transform offensive and defensive cyber capabilities "in months", not years.
What to keep in mind
The Commission confirmed AI tools were used but did not itself name ARTEX; that identification comes from CERT-EU as reported by POLITICO. No data breach affecting staff broadly has been found, but the investigation is open and findings could change.
- The Record from Recorded Future News (19 November 2026): European Commission confirms cyberattack, says hackers used AI tool
- CSO Online (19 November 2026): European Commission HR hit by cyber attack, with the FBI advisory detail
- Associated Press (19 November 2026): A cyberattack using artificial intelligence targeted the EU in October, official says